Managed Detection & Response. Always on watch.
Modern intrusions are measured in minutes, not weeks. Maverc operates continuous detection and response for organizations where a missed alert has real consequences, built on the discipline used to defend federal networks, embedded in your environment with named analysts, documented playbooks, and SLAs you can hold us to.
One view across your entire environment
Every detection is enriched, correlated, and validated before it reaches your escalation channel. When action is needed, containment happens under pre-authorized rules, in minutes.
Sample events shown. On your estate, the feed carries your telemetry, your detections, and your named analysts' decisions.
Adversaries move in minutes. So do we.
Maverc MDR connects your EDR, SIEM, identity, cloud, and SaaS telemetry into one detection fabric, then puts experienced analysts on it around the clock. We hunt, validate, and contain using playbooks your engineers helped write. Every alert is triaged, every action is logged, and every confirmed threat gets a response within SLA.
- Replace or augment an in-house SOC at a fraction of the cost to build one
- Mean time to respond measured in hours, not weeks
- Auditable evidence for cyber insurance, CMMC, and regulatory exams
- A detection library that grows stronger every month you're with us
Results your team feels
Three promises every client holds us to, week after week.
Know what needs action
Detections tuned to your environment and analysts who validate every alert before it reaches your escalation channel.
Response, not just alerts
We contain threats under pre-authorized response actions, or hand your team clear next actions. You stay in control.
Proactive defense
Threat hunts and intelligence from live campaigns feed your detection library before attackers finish their move.
Every environment under watch
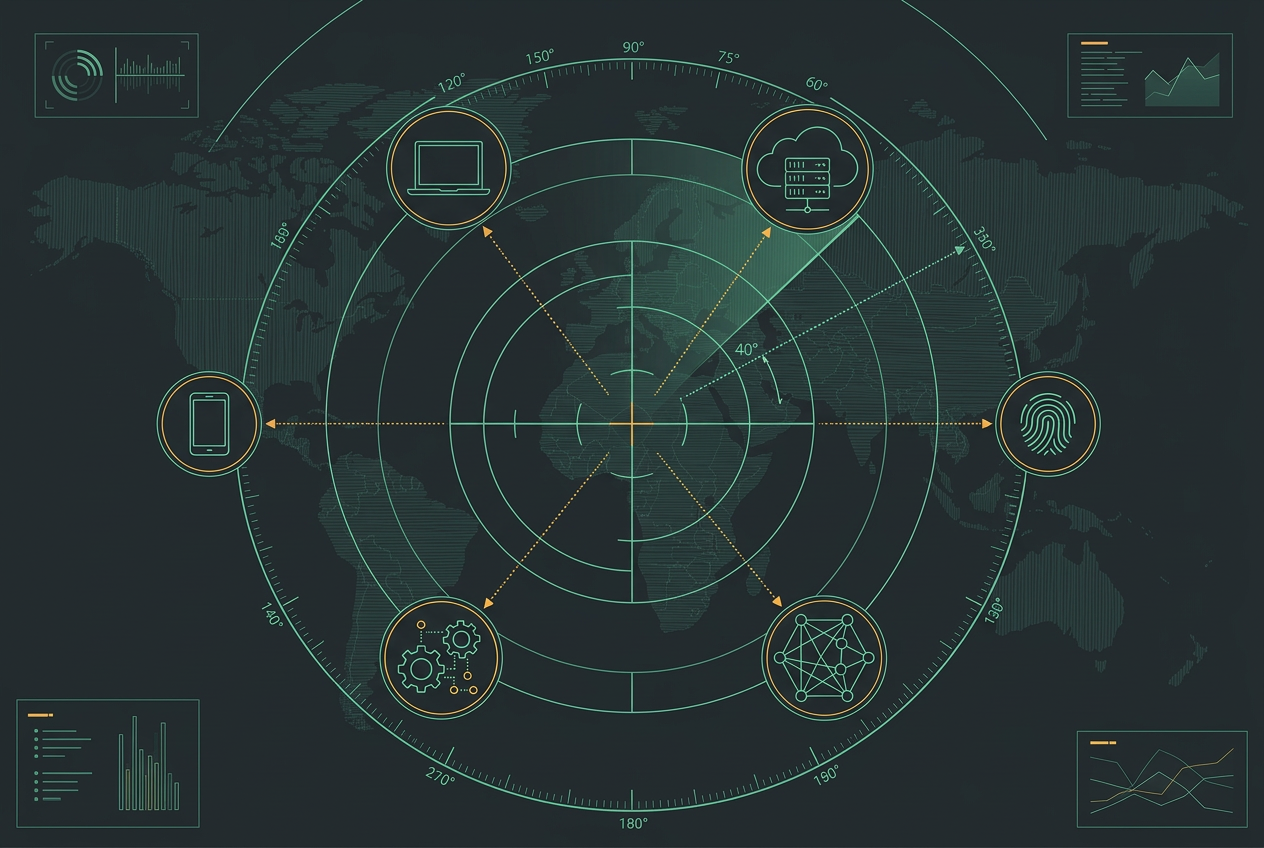
One watch floor across the environments most vendors skip, from corporate endpoints to production lines.
Endpoints, servers, and network gear
AWS, Azure, and GCP tenants
Entra ID, Okta, and on-prem directories
Company and personal devices on your network
Production floors and building systems
Microsoft 365, Google Workspace, and more
Built for missions where a missed alert isn't an option
Different sectors face different adversaries. Our watch floor is tuned to the threats and obligations that come with each.
Defense Industrial Base
Nation-state adversaries target program networks and controlled unclassified information. Monitoring mapped to CMMC and DFARS expectations, with audit-ready evidence of every response action.
Manufacturing
Ransomware that stops a production line costs more per hour than any subscription. OT-aware monitoring and containment that respects what keeps the floor running.
Healthcare
Clinical systems cannot go dark. We watch EHR, medical-device networks, and identity infrastructure with response playbooks that put patient safety first.
Financial services
Fraud, business email compromise, and exam-season scrutiny. Every alert and action documented to standards your regulators and cyber insurer accept.
SaaS & technology
Identity-first attacks against cloud tenants, CI/CD pipelines, and production data. Detection built for cloud-native estates, not yesterday's perimeter.
Five phases. One continuous defense.
Every engagement follows the same disciplined cycle used to defend federal networks.
- PHASE 01
Assess
We map your environment: crown-jewel assets, identities, cloud tenants, and the adversaries targeting your sector. Telemetry from EDR, SIEM, identity, and SaaS is brought online in 2 to 3 weeks.
- PHASE 02
Monitor
Agentic AI and analysts watch every sensor around the clock. AI agents enrich and correlate alerts while environment-specific detections and continuous hunts surface intruders that vendor defaults miss.
- PHASE 03
Validate
Every alert is triaged and validated by a human. False positives are cut, true positives escalate immediately to your named incident commander.
- PHASE 04
Contain
Pre-authorized response actions let us isolate hosts, disable accounts, revoke sessions, and block infrastructure in minutes, not after a callback.
- PHASE 05
Report
Incident reports, root cause, and new detections close the loop so the same tactic never works twice. Monthly service reviews track coverage and readiness.
End-to-end defense
Agentic AI
Autonomous AI agents triage, enrich, and correlate every alert around the clock, so your analysts start a finished investigation, not raw noise.
Continuous surveillance
Endpoint, network, identity, cloud, and SaaS under one detection fabric with full-time eyes on glass.
Detection engineering
Sigma, KQL, and SPL content written for your environment and tuned against ATT&CK, not forwarded vendor noise.
Threat hunting
Hypothesis-driven hunts informed by live campaigns against your sector, finding persistence and lateral movement.
Active response
Containment actions executed under SLA with chain-of-custody logging for every step.
Named analysts
Senior analysts and an incident commander assigned to your account who know your stack and risk tolerance.
Readiness drills
Quarterly purple-team validation and tabletop exercises that prove your defenses hold under pressure.
SLAs you can hold us to
Response actions are agreed with your team before day one, so when a threat is confirmed we act without waiting for permission.
Works with the tools you already own
Defending financial services, healthcare, federal & dib, saas, manufacturing organizations.
The adversary moves. We move first.
Maverc's Advanced Threat Unit tracks the campaigns aimed at defense contractors, manufacturers, healthcare systems, and public-sector agencies, then turns observed tactics into tuned detections on your watch floor.
What hit an organization like yours last week is already in your detection library this week.
Dispatches from the Advanced Threat Unit
- Campaigns actively targeting your sector
- New adversary tooling and tradecraft
- Vulnerabilities being exploited in the wild
- Detections shipped straight to your watch floor
Standard MDR vs. the Maverc watch floor
Same category of service. Very different posture.
- Signature-based detections catch known threats only
- Raw alerts forwarded; your team does the sorting
- Mobile and OT environments left unmonitored
- Days or weeks to investigate a single incident
- Tickets closed without explaining how it happened
- Behavioral detections and hunts stop techniques before impact
- Analysts confirm every alert; only real threats reach you
- IT, cloud, identity, mobile, and OT under one watch floor
- Incident commander engaged within minutes, not days
- Root cause and after-action review on every incident
Frequently asked questions
Put Maverc on watch
Tell us about your environment. A Maverc analyst will respond within one business day with a coverage assessment and onboarding plan.
All services